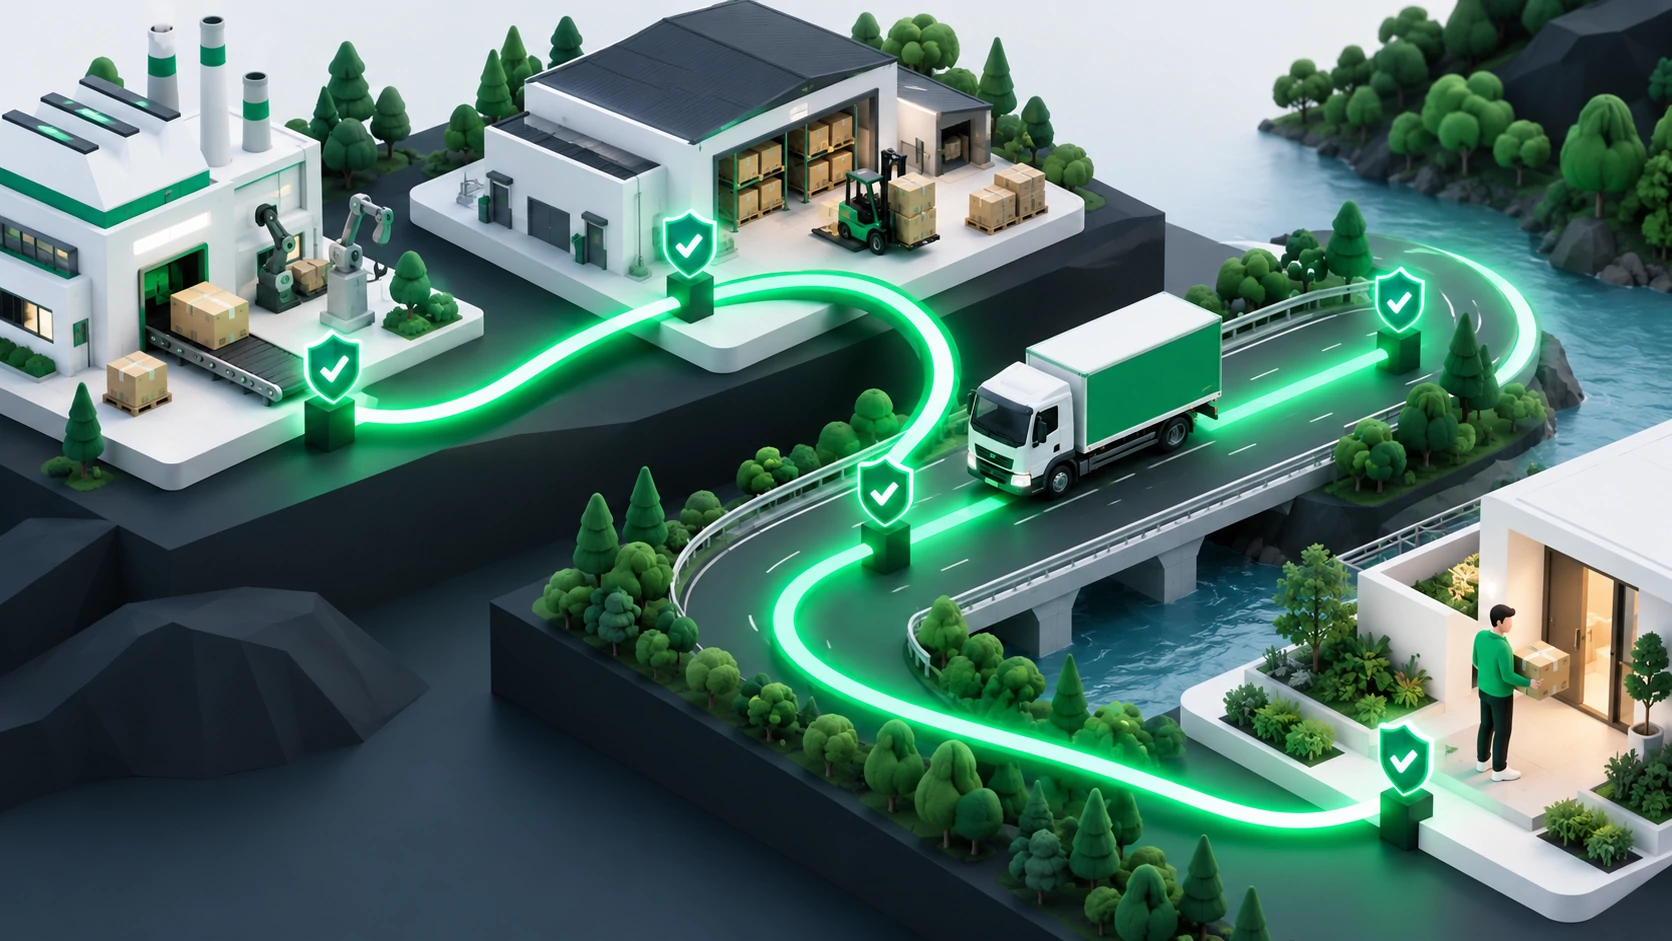
Detecting Counterfeit Spare Parts: A Guide for Brands and Distributors
Counterfeit spare-part detection cannot rely on a box, logo, or barcode alone. A defensible decision combines supplier records, item identity, packaging signals, serial or batch data, sales-channel context, and authentication history. One inconsistency may justify investigation, but it should not become an automatic counterfeit verdict.
For a brand owner, the difficult part is not merely noticing a suspicious component. It is connecting that component to the correct production, shipment, distributor, and seller records. Without those links, dealer complaints, warranty returns, and marketplace listings remain separate cases, hiding patterns that deserve attention.
Which spare-part details should trigger a review?
EUIPO's information on counterfeit automotive spare parts identifies indicators such as poor packaging, missing manufacturer addresses, inconsistent serial numbers, suspicious barcodes, spelling errors, and visible differences from genuine products. These clues support triage, but convincing packaging can still surround an unauthorised component.
A counterfeit part is not the same as an openly described aftermarket, compatible, refurbished, or used part. Misusing a brand identity to present an item as genuine is a different issue from selling a clearly labelled alternative. Review teams need this distinction or they may create false alarms while overlooking actual impersonation.
Brands can prioritise product families using their own evidence: complaint patterns, returns, warranty cases, channel deviations, and the consequences of a failure. Safety-sensitive parts and easily resold components may deserve earlier attention, but the priority should come from documented business risk rather than a generic industry assumption.
How should an evidence chain be assembled?
The first layer is the source. Purchase orders, invoices, dispatch records, authorised seller details, and receiving records should describe the same movement of goods. A recognised supplier is a useful signal, yet a supplier name alone does not authenticate the individual item inside a package.
The second layer is product and packaging identity. Compare the part number, variant, batch, serial number, manufacturer details, and package markings with the order record. If two fields conflict, place the item into a review queue instead of immediately labelling it counterfeit.
| Evidence layer | Question it answers | Its limit when used alone |
|---|---|---|
| Supply document | Through which channel did the item arrive? | It does not identify the physical unit |
| Part, batch, or serial record | Does the record match the expected product? | The printed information may have been copied |
| Packaging and workmanship | Are there physical inconsistencies? | A sophisticated imitation may look convincing |
| Unique authentication code | Does this pack match a brand record and usage history? | It does not prove technical performance |
The third layer is the manufacturer's record. Confirm that the part number exists, the claimed application is plausible, and any batch or serial data follows the expected format. Use the brand's official catalogue or authorised support channel instead of treating a general search result as confirmation.
The fourth layer is item-level authentication. When every package has a different identity, the system can assess whether the code matches a brand-issued record and whether it has appeared before. This result does not replace the surrounding evidence; it gives the team another event that can be connected to the same case.
What belongs in a counterfeit investigation record?
A useful case file is more structured than a note saying suspected counterfeit. Consistent fields allow a brand to compare incidents across dealers, locations, and product families. Access should be role-based, and the data collected should remain proportionate to the investigation.
- Product name, part number, batch, and serial number where available
- Authentication code, outcome, date, and time
- Seller, dealer, service centre, or marketplace details
- Invoice, order, and dispatch references
- Clear photographs of the package and the component
- Links to warranty, return, or customer-support records
- Reviewer, decision, rationale, and follow-up action
Photographs are evidence, not the entire decision. Lighting, camera angle, an older package design, or a legitimate manufacturing variation can create differences. Teams should compare against a current approved reference and corroborate visual concerns with identity and supply records.
If the physical item is retained, document its custody. Record who received it, where it was stored, and how it reached a technical reviewer. Preserving that context makes later quality, legal, or supplier analysis more reliable.
Why is a unique code different from a standard barcode?
A standard product barcode can be shared by every pack of the same product type. Reaching a valid catalogue page therefore does not prove that the individual spare part was released by the brand. Item-level investigation needs a serialised identity that distinguishes one package from the next.
A visible QR image can also be copied. A different code for each item, a scratch-off PIN concealed until purchase or installation, and a prior-use check can add layers against reuse. The guide to copied QR codes explains why the visible symbol should not be treated as the whole security model.
Repeated use in an unexpected place or time is a review signal, not final proof. A buyer may scan again, a workshop may verify during service, or support staff may reproduce a check. The system should show event history and context so a reviewer can distinguish routine behaviour from a suspicious pattern.
How can brands gain visibility across distributors and dealers?
When item identities are linked to dispatch records, a brand can see which code range was assigned to a distributor or dealer. Authentication outside the expected channel could reflect a legitimate stock transfer, a data error, or unauthorised selling. The signal becomes useful only after comparison with shipment and sales records.
Warranty and return workflows provide another control point. If a team can inspect identity, proof of purchase, and authentication history together, it is less dependent on a packaging photograph. The batch and serial tracking guide helps brands decide which identification level fits each product family.
Marketplace listings require a separate evidence path. A readable code in a listing image may itself be exposed to copying, while a hidden code leaves the listing without item-level identity. Brands should connect seller, order, and delivered physical item through their own records before reaching a conclusion.
What should the customer and service-centre journey look like?
Authentication instructions must be short and specific. A user should understand where the identifier appears, why a protected area must be opened, and what to do after each result. Dense security terminology can undermine an otherwise sound system by creating abandonment and poor support reports.
- Confirm the seller or service centre through the brand's official channels.
- Compare package and part numbers with the order and the relevant vehicle or equipment.
- If offered by the brand, check the unique QR code and concealed PIN through the official application or page.
- For a repeated, invalid, or mismatched result, stop before installation and contact official support.
- Keep the invoice, packaging, and result screen until the review is complete.
Türkiye's Ministry of Trade advises consumers to verify authorised service details through the manufacturer's official website or SERBİS. That check helps validate the service channel; it is not, by itself, an item-level spare-part authentication method.
Result screens should distinguish valid, previously used, not found, and technical error outcomes. A missing record should not instantly become a counterfeit accusation. Data synchronisation, a mistyped value, or a code that has not yet been activated may require a support path.
Where does xBarkod fit in this control model?
xBarkod supports item-level package authentication through a unique QR code and a concealed scratch-off PIN for each product. As a customer checks a code, the company dashboard can help reviewers examine the time, location information, and prior-use history of the event. Those records are most useful when interpreted with shipment and channel data.
When assessing the xBarkod product authentication approach for a spare-part family, test it with real packaging, real dispatch steps, and realistic support cases. The objective is not to assume that one technology eliminates counterfeiting; it is to turn previously invisible item and authentication events into evidence the brand can manage.
How should a pilot be designed?
A strong pilot begins with a precise question rather than the largest possible volume. Choose one product family, a limited channel, and a named review team so code creation, labelling, dispatch, authentication, and case closure can be observed end to end. Launching across many distributors at once can obscure the source of an error.
- Select the product family and the risk scenario to be tested.
- Assign responsibility for code creation, printing, waste control, and dispatch.
- Test first use, repeated use, invalid codes, and offline support scenarios.
- Name the owner of each case across dealer, support, quality, and brand-protection teams.
- Review data integrity, customer messages, and closure evidence together.
Successful scanning should not be the only acceptance criterion. The test should confirm that the right product record appears, the code is attached to the intended package, the expected event reaches the dashboard, the customer receives a clear message, and the team can close the case with a recorded rationale.
What should happen after a suspicious authentication?
Start by classifying the signal as a data issue, operational error, customer repeat, channel mismatch, or possible counterfeiting. Bring the related dispatch, sale, product, and authentication records into one case. Avoid accusing a dealer or customer before the supporting evidence is complete.
- Stop use and involve the appropriate specialist if there may be a safety risk.
- Compare the code with batch, serial, order, and dispatch records.
- Confirm the seller or service authorisation through an official channel.
- Inspect the physical sample against an approved reference if necessary.
- Record the decision, evidence, and follow-up action in the case file.
Authentication data should be available only to teams with a legitimate need. If location or user information is involved, the purpose, retention period, permission model, and access controls need separate consideration. Product authentication does not remove the brand's responsibility for sound data governance.
Which implementation mistakes weaken detection?
One common mistake is treating professional packaging as proof of authenticity. Another is labelling every repeat scan as counterfeit. The first overlooks a well-made imitation; the second ignores valid behaviour and floods the team with avoidable alerts.
Brands also confuse printing a code with implementing a control system. Unused codes and print waste must be reconciled, code ranges must be connected to dispatches, result messages must be tested, and every alert must have an owner. A label without those processes cannot create a complete chain of control.
Finally, authentication and technical conformity are different questions. A valid identity record does not establish fitment, performance, or compliance with every safety requirement. Manufacturer instructions, quality controls, and relevant technical procedures must address those matters separately.
Frequently asked questions about counterfeit spare-part detection
Does scanning a barcode prove that a spare part is genuine?
No. A general barcode often identifies a product type and may be shared across many packages. Item-level checks require a serialised identity, a brand-issued record, and prior-use history, interpreted with supplier, document, packaging, and product evidence.
Can a part in convincing packaging still be counterfeit?
Yes. Printing, logos, and labels can be imitated. Packaging assessment should be supported by purchase records, part numbers, serial or batch details, and a unique brand authentication code where one is available.
Does a second use of the same code prove counterfeiting?
No. A repeat event is an important risk signal, but a customer rescan, workshop process, or support test may provide a legitimate explanation. Review the time, location, channel, and earlier events before reaching a decision.
Are aftermarket and counterfeit parts the same?
No. A clearly described compatible or aftermarket product is different from an item that impersonates another brand and is presented as genuine. Whether an alternative part is suitable and safe remains a separate technical assessment.
Which product family should a brand protect first?
Start where the brand's own complaints, returns, warranties, channel exceptions, and potential safety consequences show the clearest risk. A limited pilot makes it easier to verify whether identity and case-management processes work in daily operations.
Can QR codes and scratch-off PINs eliminate spare-part counterfeiting?
No single layer removes every risk. Unique QR codes, concealed PINs, and prior-use checks can reveal reuse and suspicious activity. Their value depends on controlled code handling, correct label application, reliable data, and consistent case review.
Conclusion: Turn a visual suspicion into manageable evidence
Counterfeit spare-part detection becomes stronger when packaging, supply records, item identity, authentication history, and channel context form one decision chain. Structured case records and clear ownership help the brand focus on credible risks while reducing false alarms.
Map the identity and channel journey of one exposed product family first. If item-level evidence is missing, consider a limited xBarkod pilot and measure what the code contributes from packaging and dispatch through customer support and case closure.
More Articles
How to Detect Reused Product Codes: A Daily Workflow for E-Commerce Brands
Learn how e-commerce brands review reused product codes through unique identities, verification flows, dashboard events, and suspicious-use checks.
Cosmetic Product Authenticity Checks: What Does Each Signal Prove?
Learn what registries, barcodes, batch details, packaging checks, and unique item codes can prove when verifying cosmetic product authenticity today.
Product Authentication for SMEs: A Practical Starting Plan for Small Brands
Learn how SMEs can scope product authentication, control costs, test labels, run a practical pilot, and build a manageable daily review process well.