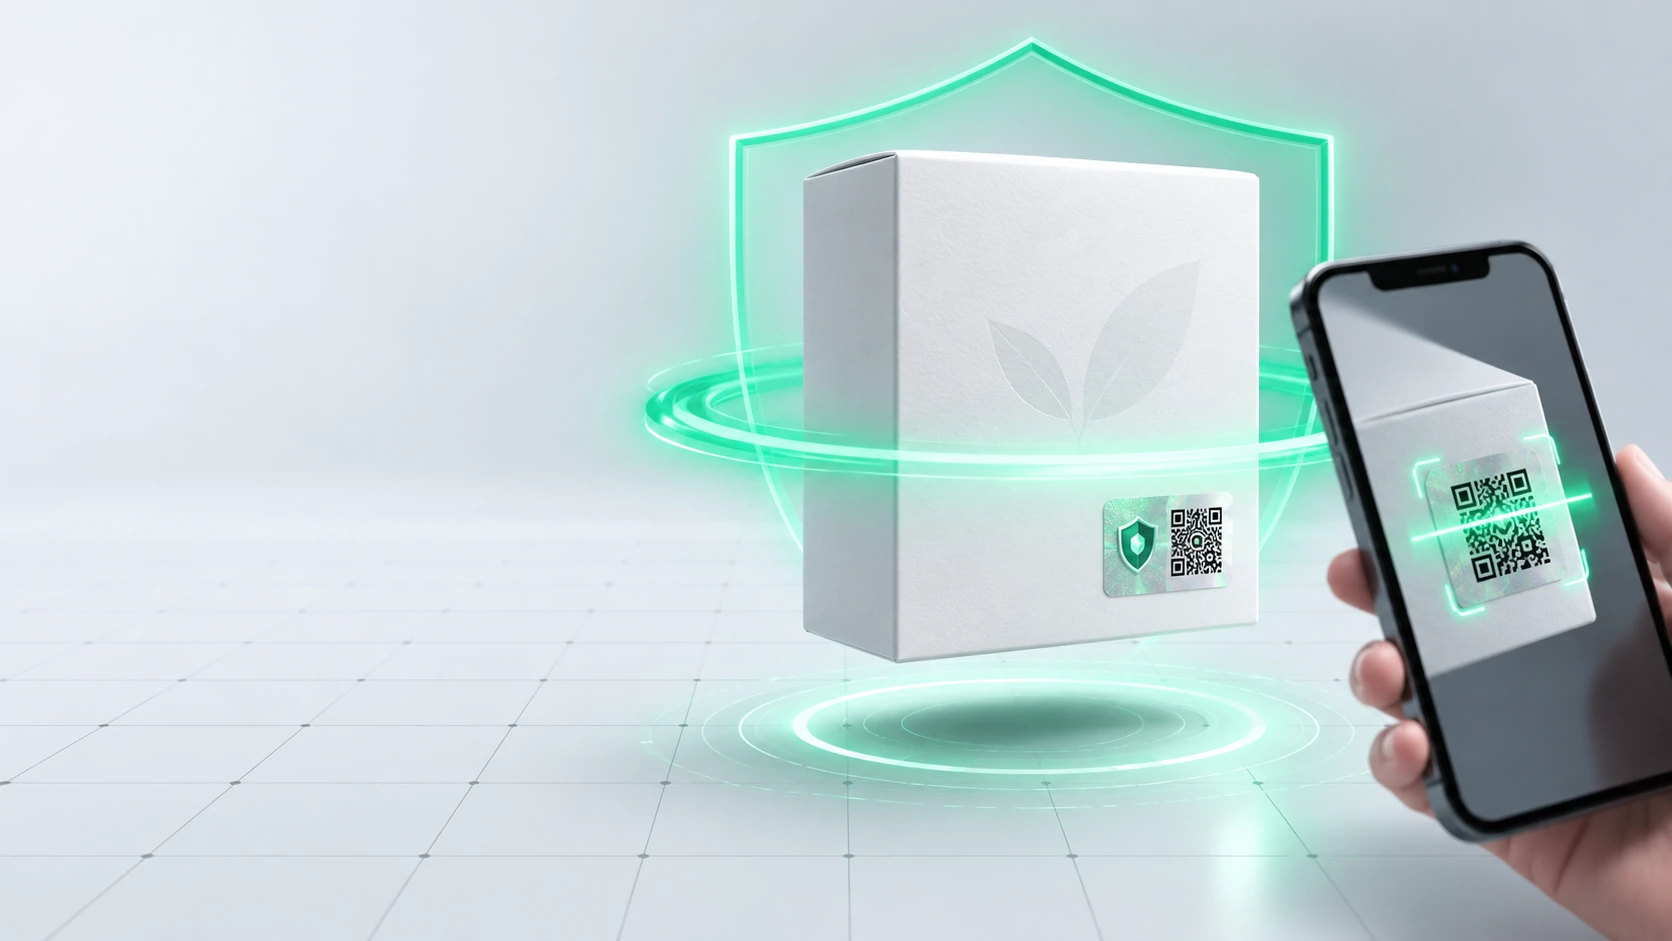
Supplement Product Authentication: From Regulatory Approval to Item-Level Control
Supplement product authentication is not a single barcode check. A reliable process separates the product's official approval record from packaging and batch consistency, seller context, and the link between the individual pack in hand and an identity issued by the brand. Each layer answers a different question.
For a brand owner, the goal is broader than showing a green result to a customer. The company must define which record belongs to which product, how a suspicious check will be reviewed, and where regulatory approval ends and pack-level evidence begins. Authentication then becomes an operating control rather than an unsupported marketing claim.
What is the searcher actually trying to verify?
Current Turkish search results show a strong need to determine whether a supplement appears on the Ministry's approved list. The Turkish Ministry of Agriculture and Forestry explains in its official consumer notice that the current list is available through the Food Safety Information System and includes product, company, and approval-status information.
That check is necessary, but it operates at product level. The public listing does not provide the event history of the particular bottle or box held by a customer. A listing should therefore not be treated as proof that a pack has not been copied or that it moved through an authorised sales route.
A sound process keeps the needs separate. First, verify the official approval status. Next, examine the physical pack and any item-level identity issued by the brand. Result screens and support scripts should state clearly which layer was checked.
How does a three-layer authentication model work?
No single query answers every question about a supplement. The official record concerns the approved product and business. Batch and packaging records describe a production group. An item identity distinguishes the pack presented for review. Combining the layers prevents any one signal from carrying a conclusion it cannot support.
| Control layer | Question answered | Limit when used alone |
|---|---|---|
| Official approval listing | Does the product appear on the approved list? | It does not show the history of this individual pack |
| Batch and packaging record | Does the pack fit the expected production group? | It does not distinguish every unit in that batch |
| Item authentication code | Does this pack match a brand record, and has the code been used? | It does not replace regulatory approval or quality testing |
| Sales-channel record | Does the product fit the expected seller and dispatch route? | It does not prove the physical contents |
When those limits accompany the result, customers and support teams can act appropriately. “Listed as an approved product,” “code matches a brand record,” and “repeat use requires review” are not interchangeable messages.
What is the correct order for checking official approval?
The Ministry's supplement information page says that supplements require approval and that the approved list can be searched by manufacturer or importer, approval number, or product name. A brand can make the route to this official check visible without presenting its own page as a government service.
- Locate the product name, brand, and supplement approval number on the packaging.
- Compare those details with the approved-product list in GGBS.
- Check whether the product, company, and approval status align with the label.
- If no result appears, review spelling and number entry before using an official reporting route.
The Ministry also explains that approval is product-specific. Approval for one item from a company does not mean that every item in its portfolio is approved. Brands should map each product separately and avoid using another product's record as a general trust mark.
The same official page states that supplements are not medicines and are not intended to prevent or treat disease. An authentication result should not turn identity evidence into a therapeutic promise, nor should approval status be presented as a laboratory result for the contents of one pack.
Why are batch codes, barcodes, and item identities different?
A general product barcode is usually shared by every pack of the same trade item. A batch number distinguishes a production group. An item-level identity distinguishes two packs that belong to the same product and the same batch. The required level depends on the decision the brand needs to make.
The GS1 Global Traceability Standard distinguishes product-class, batch, and fully serialised identification. It explains that instance-level identification can represent each individual product occurrence. This makes clear why a product barcode alone cannot provide a separate authentication history for every physical pack.
The right design does not discard the existing barcode. The product identifier names the trade item, the batch identifies a production group, and the authentication identity distinguishes the pack. These records must meet in consistent master data; otherwise a valid code may still be attached to the wrong product or batch.
What evidence should item-level authentication create?
Pack-level authentication becomes useful when each protected item receives a separate identity. Because a visible QR image can be copied, a brand may add a concealed PIN that remains hidden until the customer opens it and review previous-use history. These controls produce evidence for review; they do not guarantee authenticity in every circumstance.
- The product and variant assigned to the code
- The related batch or production record
- Whether the identity is active, cancelled, or unused
- The timing of first and repeat authentication events
- Location context within user consent and technical accuracy limits
- The result shown to the customer and the support route offered
A previously used code does not prove counterfeiting by itself. The customer may have scanned twice, a support agent may have performed a check, or the code image may have been copied to another pack. The brand should distinguish these explanations with product, order, time, location, and case records.
How should the internal data flow be organised?
Authentication is more than the customer-facing screen. The company needs a minimum reliable relationship among product master data, official approval, batch, code issuance, label application, dispatch, sales channel, and support cases. Not every system must be merged, but the owners and meanings of decision-critical fields must be explicit.
Begin by naming the team responsible for matching products to approval numbers. Then document who issues codes, when activation occurs, how damaged or unused labels are reconciled, and who owns a suspicious event. A sophisticated dashboard will not become a daily control if no role owns the decisions.
When production is outsourced, the brand and manufacturer should allocate responsibility for code files, print permissions, label delivery, waste, reprints, and activation. If the physical label separates from the digital record on the line, even a customer scanning the correct pack may receive a misleading result.
How should a packaging and production pilot be designed?
Supplement packaging may use a bottle, carton, pouch, or several layers together. Label placement should account for how the pack opens, curved surfaces, friction, moisture, light, and the point at which the customer sees the code. A code that works in artwork must still be tested in production and distribution conditions.
The security-label application guide connects surface choice, placement, readability, and line controls. A pilot should deliberately include intact, damaged, misapplied, cancelled, and rescanned codes rather than testing only the ideal path.
The objective is to discover faults safely, not to stage a flawless demonstration. Real packaging, a normal production shift, and the support team should participate in the same flow. Acceptance should depend on recording and routing failures correctly as well as on successful scans.
How should customer results be written?
A result must name the layer that was checked. “The code matches a brand record” and “the product appears on the Ministry's approved list” are supported by different evidence. Substituting one for the other creates false certainty and makes later investigation harder.
Valid, previously used, not found, and technical-error states need different wording. Give the customer a safe next step and explain why a photograph, seller, receipt, or batch detail may be required. A suspicious event should not trigger an unsupported accusation against a product or seller.
Instructions should also remain short: where to find the official approval number, how to scan the QR code, when to reveal the concealed field, and which official brand channel to contact. The customer should not need to understand the company's system architecture to complete a responsible check.
How should a suspicious authentication be investigated?
Incident handling matters more than displaying an alert. A code may be missing because of data entry, delayed activation, or a product mismatch. Repeat use may be legitimate or may indicate copying. An unexpected location needs dispatch and channel context before it supports any conclusion.
- Classify the event provisionally as a technical fault, data mismatch, legitimate repeat, channel exception, or possible copying.
- Collect the product, approval, batch, code, dispatch, seller, and support records in one case.
- Confirm that the customer result and dashboard record describe the same event.
- Inspect the physical pack and proof of purchase when necessary.
- Record the decision, reasoning, action, and owner responsible for closure.
Closed cases should improve the process. Repair master data after a product mismatch, change application after label damage, and revise wording when customers misunderstand a result. The system then exposes operational weaknesses instead of merely accumulating alerts.
Where does xBarkod fit in this control plan?
xBarkod supports a unique QR code and concealed scratch-off PIN for each product, checks previous code use, and makes authentication events visible in a company dashboard. Those functions can add item identity and event visibility without replacing the official approval search.
Evaluate the xBarkod product authentication approach in the real flow of one product family. The pilot should cover product-to-approval mapping, label application, first authentication, repeat use, dashboard review, and support closure as one connected process.
The QR code and scratch-off PIN implementation guide explains how visible and concealed factors relate to the code lifecycle. The choice should be based on the documented risk and daily ownership, not on label appearance alone.
What should the pilot acceptance criteria cover?
Use evidence from the company's own process instead of inventing success rates or sales claims. A pilot creates useful decision data when product, code, and batch matching can be verified, customer results are understood, suspicious events reach the correct team, and cases close with documented evidence.
- Every code resolves to the correct product and, where relevant, batch
- The label remains readable through production, transport, and sale
- Waste, cancellation, and reprint records can be reconciled
- First use, repeat use, invalid, and technical-error outcomes remain distinct
- Support can collect the required evidence and close the case
- Official approval and brand authentication are explained as separate checks
Expand only after these controls work in normal production. When a new item, manufacturer, or channel enters scope, repeat the acceptance scenarios. A result from the first pilot should not be treated as automatic evidence that every later deployment is suitable.
Which mistakes weaken supplement authentication?
The most serious mistake is presenting an approved-list entry as definitive proof about the pack in hand. The reverse is also wrong: a valid item code issued by a brand does not replace regulatory approval or content analysis. The layers work together and should never impersonate one another.
Other common failures include placing the same QR code on every pack, failing to connect codes with product and batch data, exposing a concealed field before sale, mixing test scans with customer events, and leaving alerts without an owner. Daily control discipline matters as much as the technology.
Frequently asked questions about supplement product authentication
Does a GGBS listing definitively prove that a pack is authentic?
The approved-product list is used to check product, company, and approval-status information. That public record does not show the event history of the particular pack held by a customer. Packaging, batch, seller context, and any item identity issued by the brand require separate review.
Is a barcode search the same as item-level authentication?
No. A general barcode normally identifies a product type and may appear on many packs. An item identity connects each pack to a separate record, allowing first and repeat authentication events to be considered for that unit.
Why use a scratch-off PIN on a supplement?
A visible QR image can be copied, so a PIN concealed until the customer opens it can add a second factor. It is not a guarantee by itself and should be combined with secure issuance, correct pack matching, use history, and incident review.
Does a second use of the same code mean the product is counterfeit?
Not always. A customer may rescan, support may test the pack, or the code may have been copied. The brand should examine time, location, order, seller, and support context before distinguishing a legitimate repeat from suspicious use.
Should the official approval search appear in the authentication journey?
Showing the official GGBS route can help users, but the brand screen must not imitate a Ministry service. Official product approval and the brand's item-code check should have separate labels, explanations, and clear limits.
Which product should an authentication pilot start with?
Choose one product family with a documented complaint, channel uncertainty, or copying risk, packaging suitable for a controlled label trial, and an accessible production team. The starting decision should come from the brand's evidence rather than a generic industry claim.
Conclusion: Do not confuse approval with pack evidence
Supplement product authentication becomes reliable when it begins with the official approval check and then connects product, batch, packaging, sales-channel, and item-code evidence in the correct order. Every result should state what it proves and what remains outside its scope.
Map one product family's path from its GGBS record to support-case closure. If pack-level visibility is missing, plan a limited xBarkod pilot and base expansion on correct matching, understandable outcomes, and incidents that can be closed with evidence rather than broad promises.
More Articles
Enterprise Brand Protection Systems: A Scalable Control Guide
Learn how to scale enterprise brand protection across product identity, channels, team ownership, integrations, authentication, and incident review.
How to Detect Reused Product Codes: A Daily Workflow for E-Commerce Brands
Learn how e-commerce brands review reused product codes through unique identities, verification flows, dashboard events, and suspicious-use checks.
Detecting Counterfeit Spare Parts: A Guide for Brands and Distributors
Learn how brands and distributors combine supplier, packaging, serial, channel, and item-level authentication evidence to detect counterfeit spare parts.