QR Code Authentication Security: A Daily Workflow for Import Brands
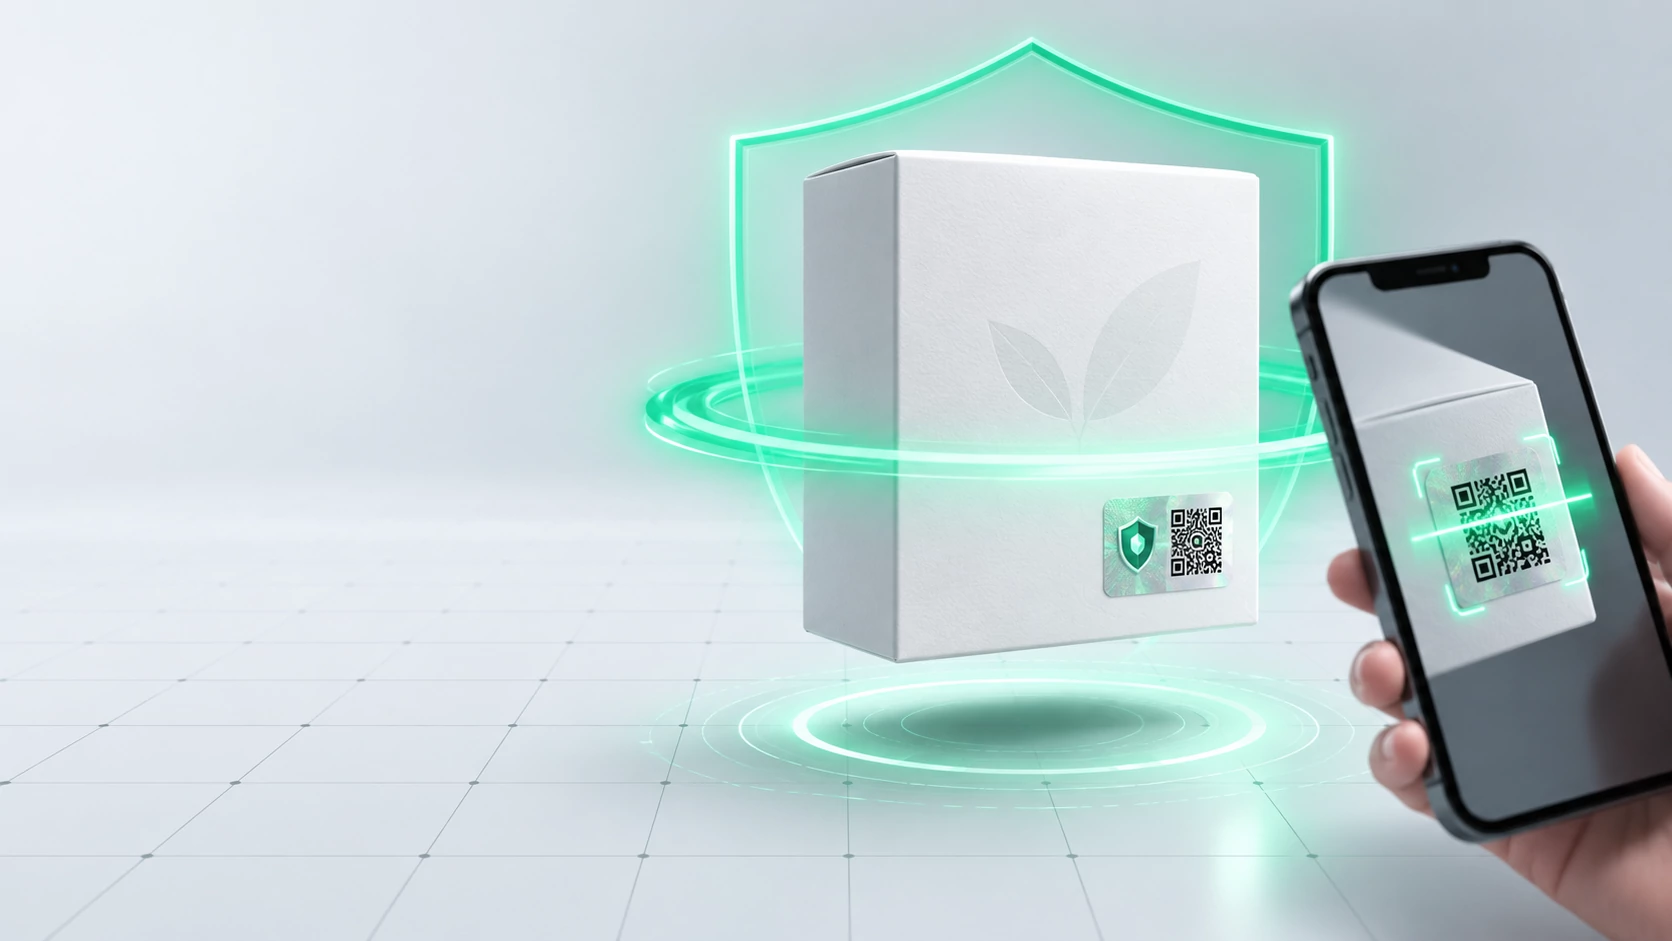
QR code authentication security is more than making a symbol scannable on an imported product. A reliable workflow connects the correct product record to a unique code, keeps the concealed PIN protected until customer use, explains the authentication result clearly, and reviews dashboard activity against the brand's own operating records.
An import brand may not manufacture the item, but it still owns the meaning of the identity placed on the pack. The practical value of daily authentication is that a field check becomes a reviewable brand signal. The signal supports investigation; it does not create a conclusive judgment on its own.
Security begins before the QR image
Not every QR code on packaging is an authentication control. A code may open a product page, a manual, or a shared campaign. For authentication, the important question is whether the visible carrier leads to the official brand flow and whether a valid record exists for that specific saleable item.
A security review therefore looks beyond scanning. It asks which product record sits behind the code, whether the concealed PIN remained covered, how prior use is communicated, and how the event appears in the company dashboard. These controls form one workflow rather than separate features.
Separate the import record from the item identity
A general product barcode may repeat across packs of the same item type. GS1's explanation of unique identification distinguishes base product identification from the identity of an individual instance. When an import brand needs an item-level authentication history, it needs an identity that separates one pack from another.
The brand's product record should keep the product name, packaging version, and relevant internal batch or shipment reference consistent. To compare xBarkod activity with those company records, the business must document which code allocation was applied to which physical products.
Without that distinction, a valid code may still be difficult to reconcile with the pack carrying it. The authentication service can evaluate code validity and prior use. Correctly linking the physical pack, the approved product record, and the assigned label remains an operational responsibility of the brand.
Build coding around an approved record
The xBarkod flow uses a unique QR code and a concealed scratch-off PIN for each protected product. The import brand first confirms the product record to be labelled, then allocates the received labels to the correct packaging group. The future authentication event can then point back to a meaningful product identity.
Label application might happen at an external warehouse, a packing location, or inside the brand's own operation. Wherever it happens, the same controls apply: the label must reach the correct product, the QR area must remain readable, and the concealed PIN must stay covered before customer authentication.
Daily control should connect the following records:
- The approved product and packaging record assigned to the label
- Labels released for application and labels left unused
- Damaged, misapplied, or cancelled labels
- The receiving and dispatch context of the labelled goods
- The team responsible for reviewing an application exception
This list does not imply extra dashboard features. It defines the evidence the import brand maintains around the xBarkod identity, so dashboard activity can be reconciled with a physical item and a company record.
Why the concealed PIN is an operating control
The QR code stays visible on the package while the scratch-off PIN remains concealed until authentication. This adds hidden information to the visible carrier. The customer scans the QR code with the xBarkod App, enters the PIN, and receives the authentication result.
The brand should check that the concealed area remains intact through receiving, storage, and dispatch. A PIN area that is open, damaged, or inconsistent with the package is not automatic proof of a counterfeit. It is a packaging exception that should be explained before the product is released for sale.
Because the label can be applied to existing product packaging, placement also matters. The QR area should be readable, the PIN covering should not be opened accidentally, and the package should make the official authentication route clear to the customer.
What should the customer authentication flow include?
The customer journey is deliberately direct. The customer scans the QR code in the xBarkod App, opens the scratch-off area, enters the concealed PIN, and views the result. If the code shows prior use or another suspicious condition, the user can be warned.
- Check that the security label appears in the brand's designated package position.
- Scan the QR code with the xBarkod App.
- Open the scratch-off area and enter the PIN.
- Compare the product and use information on screen with the physical pack.
- Keep the packaging and purchase context when an unexpected result requires brand support.
A valid result shows that the label code matches a record defined by the brand and communicates the PIN's use status. It should not be presented as an independent test of product contents, proof of an import document, or conclusive evidence for the complete supply chain.
The result message should protect that boundary. A customer needs more than a coloured symbol: the flow should support comparison with the product, explain prior use, and provide an official route to the brand when the result is unexpected.
How should the brand read dashboard activity?
The xBarkod company dashboard helps the brand follow authentication activity with product, time, and location information, including prior-use context and suspicious movements. This visibility gives the import brand a defined item identity from which to begin a review.
A dashboard event is not a decision. The brand first confirms the product record behind the code, then compares the use history with its receiving, dispatch, order, return, and support records. Location should also be treated as a contextual signal because its meaning depends on permission and device conditions.
A daily review can use questions such as these:
- Does the code match the approved product and packaging record?
- Can prior use be explained by the customer or support journey?
- Are time and location consistent with the known dispatch or sale context?
- Has the same identity been reported on different physical packs?
- Is packaging evidence or purchase context available for review?
This turns the dashboard into an operating tool that helps order the investigation. Explainable activity can be closed with a reason. Unexplained activity becomes a case for additional evidence rather than an immediate accusation.
How can suspicious use be separated from normal activity?
A repeated authentication does not always mean that a code was copied. A customer may revisit the result, a support team may help check the product, or a returned item may be scanned again. Prior use becomes meaningful only when it is considered with the item, time, location, and company evidence.
Activity deserves closer review when the same identity appears on different packs, on-screen product information does not match the package, or the movement cannot be reconciled with company records. These are risk signals. They are not laboratory or legal findings that xBarkod makes by itself.
The review record should state which dashboard information was considered, which company evidence was checked, and why the event was closed or escalated. Operations, customer support, and brand protection teams can then work from the same facts instead of separate assumptions.
Where does xBarkod fit into daily work?
xBarkod enables an import brand to use a unique QR code and concealed scratch-off PIN on each protected product, lets the customer authenticate through the xBarkod App, and gives the company dashboard visibility into authentication activity. The operational benefit is one identity connecting coding, customer checks, and brand review.
Before evaluating the xBarkod product authentication flow, the brand should define its product records, label application point, and ownership of suspicious-activity review. It can then test QR readability, PIN concealment, valid results, prior use, and dashboard recording on actual packaging.
The system does not replace customs, inventory, order, or warehouse management. Records from those systems provide the business context used to interpret a field authentication event. Secure practice depends on keeping those responsibilities clear while connecting the evidence.
How should security boundaries be protected?
Authentication language should avoid false certainty. A valid code indicates a label identity matching a brand-defined record. Prior use indicates that the same concealed credential has already been submitted. Both results still require the physical item, package, and sale context to be considered.
Operational ownership also needs to be explicit. The team governing product records, the team controlling label application, the team reviewing dashboard activity, and the team communicating with customers should use the same decision rules.
- Check the product-to-code assignment before dispatch.
- Route products with exposed PIN areas into an exception process.
- Do not turn a dashboard signal into a conclusion without company evidence.
- Show customers the official app and support route.
- Record the reason behind every suspicious-activity decision.
Frequently Asked Questions about QR code authentication security
What does QR code authentication security mean?
It means linking a unique code to the correct product, keeping the PIN concealed until customer use, explaining the result clearly, and making the event available for company review. A scannable QR code alone does not create a secure authentication workflow.
What happens if the visible QR code is copied?
In the xBarkod flow, the visible QR code is accompanied by a concealed scratch-off PIN. The customer submits the PIN during authentication, and the system checks validity and prior use. Unexpected reuse becomes a signal for the brand to review with other records.
Does a valid result conclusively prove that the product is genuine?
The result confirms that the label code matches a record defined by the brand and communicates the PIN's use status. Product contents, import documentation, physical packaging, and sales context may still require separate checks.
Does dashboard location identify the seller?
No. Location is a signal attached to an authentication event; it does not automatically prove a seller or channel identity. The brand should compare it with dispatch, order, and support records before drawing any conclusion.
Is every prior-use warning suspicious?
No. A repeated customer check, support activity, or a return process may explain another authentication. The item identity, time, location, and operating evidence should be considered together to decide whether more review is needed.
Does xBarkod replace import records?
No. xBarkod makes the authentication identity and related activity visible. The import brand continues to manage product, receiving, dispatch, order, and return records in its own systems and uses them to interpret dashboard signals.
Conclusion: carry security from code to review
For an import brand, QR code authentication security combines the correct item identity, an intact concealed PIN, a clear customer journey, and dashboard events reviewed with evidence. This connects a packaging control to daily brand operations without overstating what a single scan can prove.
Before rollout, the brand should test its product record, label position, and review ownership on real packaging. Reading the guides on copied QR code risk, reused product codes, and dashboard review together helps define those operating boundaries.
More Articles
Product Authentication Code Mapping: A Daily Workflow for Private Label Brands
Learn how private label brands map authentication codes to products, manage QR and hidden PIN checks, review dashboard activity, and investigate suspicious use.
Product Authentication System Setup: A Daily Workflow for E-Commerce Brands
Set up product authentication with clear records, unique codes, QR and hidden PIN checks, dashboard review, and suspicious-use handling for e-commerce brands.
Product Authentication Location Tracking: From Setup to Daily Review
Build product authentication location tracking with clear permissions, data quality, daily review, privacy controls, and practical pilot criteria.