Brand Protection in Contract Manufacturing: Label and Overrun Controls
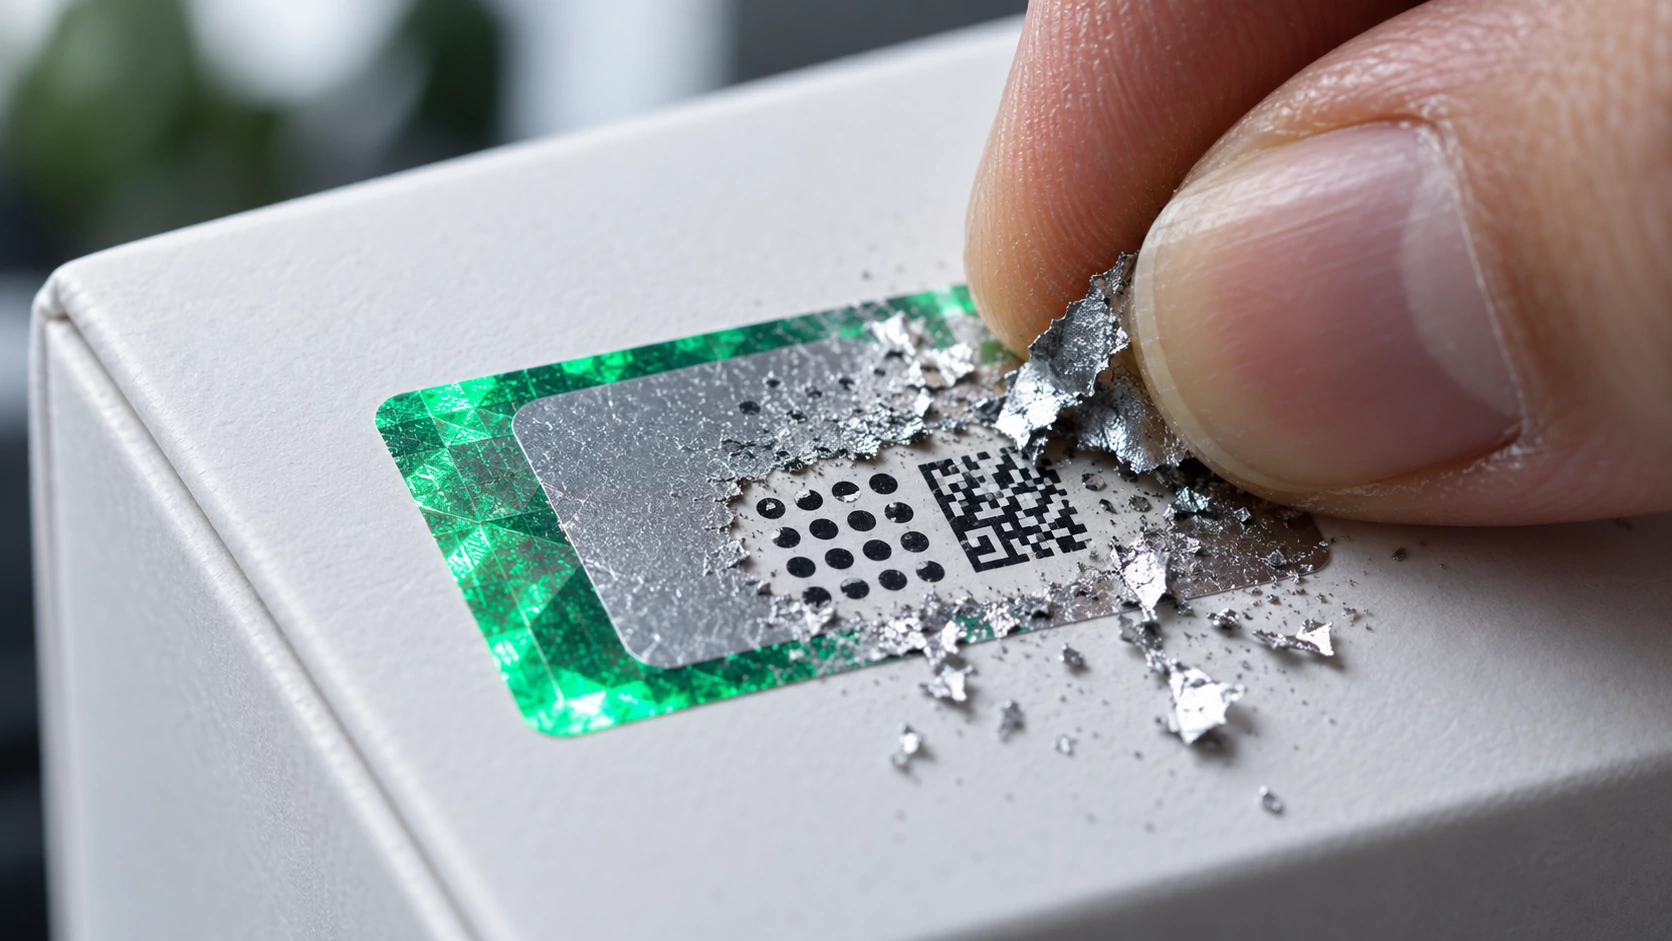
Brand protection in contract manufacturing means controlling more than the logo on the finished pack. The brand must connect approved packaging, security labels, and unique product identities to a specific production order, then account for every identity that was applied, rejected, left unused, returned, or destroyed.
The decisive moment is often the close of the order rather than its release to the factory. If accepted goods, applied labels, packaging scrap, unused codes, and dispatched quantities cannot be reconciled, the brand may struggle to investigate a questionable item found later in the market.
A sound control model does not assume that the contract manufacturer is the threat. It assigns authority, evidence, and exception handling before production begins. Quality, traceability, and authentication can then support one another without being treated as interchangeable systems.
Where does brand exposure arise at a contract site?
Exposure is not limited to deliberate overproduction. An obsolete artwork may reach the line, a security label may be applied to the wrong variant, cancelled identities may be reopened, rejected prints may lack disposal evidence, or leftover labels may be mixed into a later order. Each failure weakens the link between brand approval and the physical item.
Controls therefore begin before finished-goods inspection. The product master, approved artwork, production order, batch or serial rule, and brand-controlled identity material should point to the same job. A product barcode, a batch number, and an item-level authentication code serve different purposes; the work instruction should not blur them together.
Define the assets that require brand approval
The brand should identify which assets cannot be created, changed, or consumed without explicit authority. GS1 explains that the brand owner, meaning the organisation that owns the trade-item specifications, is normally responsible for allocating the GTIN regardless of where the item is made. That principle is a useful governance baseline, while unique authentication identities still need their own ownership and permission rules.
- Approved product and packaging versions
- Brand artwork, logos, and printing tools
- Product barcode, batch, and serial rules
- Unique QR and concealed scratch-off PIN labels
- Rejected, cancelled, and unused identities
- Dispatch, return, and destruction evidence
The asset register can sit in a controlled instruction or contract schedule, but a document alone does not operate the line. Teams also need to know which artwork is current, who can allocate codes, who receives security labels, and who approves the final reconciliation. These decisions must be visible in routine work, not only during an audit.
Run code and label allocation as a closed loop
A closed loop prevents brand identities from becoming an unrestricted pool at the factory. A defined allocation is opened for each production order. Received, applied, rejected, unused, returned, and destroyed identities are recorded in separate states, allowing the identity lifecycle to close alongside the quantity of finished goods.
- Link the approved product and packaging version to the order.
- Allocate a controlled code or label range through an authorised role.
- Record receipt with the date, batch, and responsible person.
- Separate application errors and printing waste as they occur.
- Block, return, or securely destroy identities that will not be used.
- Approve the final reconciliation with quality release and dispatch evidence.
A factory or service provider may technically generate codes. The brand should still be able to inspect duplicate-prevention rules, allocation limits, cancellation actions, and an audit trail. The same principle applies to printers and label suppliers: possession of an artwork file should not create unlimited authority to produce brand identities.
What evidence should close the production order?
The GS1 Global Traceability Standard describes critical tracking events and the key data elements that explain them. In a contract operation, receiving, transforming, packing, releasing, shipping, and destroying are practical events to record with who, what, where, when, and why context.
| Control point | Expected evidence | Question to close |
|---|---|---|
| Material receipt | Label or code range, receiver, date | Which identities entered the site? |
| Application | Product version, order, applied quantity | Was the identity linked to the right item? |
| Waste and errors | Reason, status, block or destruction record | Was the unusable identity closed? |
| Quality release | Accepted batch or serial scope | Which goods may enter saleable stock? |
| Dispatch | Recipient, date, related identities | Where did accepted goods go? |
Balanced totals are not enough. A label can be applied to the wrong product version while the count still appears correct. Closing the order should test both quantity reconciliation and the relationship among a sample item, its code, packaging version, product record, quality decision, and shipment.
Control overruns, rejected packs, and unused material
An approved production tolerance is not the same as uncontrolled overrun. If the order allows a tolerance, define the limit, approval role, identity treatment, and release decision before manufacturing starts. Samples, second-quality goods, and unapproved output also need clear rules for when brand packaging may remain attached.
Rejected labels and branded packs should not disappear into a generic waste total. Their identities should be made unusable, the corresponding digital records should be closed, and return or destruction evidence should be retained. Intact unused labels should not roll automatically into the next order; the brand should explicitly reallocate them.
Connect a field signal to the factory record
When a questionable product appears, validity of the visible code is only the first check. The brand should ask which order, product version, batch, and shipment the identity belongs to; whether prior use exists; and whether the observed packaging matches the approved version. Production-close evidence now becomes investigation context.
A repeat authentication, unexpected location, or product mismatch is a signal rather than proof of overproduction or counterfeiting. A customer may scan twice, support may perform a test, or location permission may be limited. The brand needs to compare the authentication event with production, dispatch, return, and support records before deciding what happened.
Preserve relevant photographs, proof of purchase, and the authentication result before changing the status of the identity. If the incident may lead to legal action, obtain advice for the contract and jurisdiction involved. Technology can surface risk and preserve records; it cannot issue a final legal finding on its own.
Where does xBarkod fit?
The xBarkod product authentication system supports a unique QR code and concealed scratch-off PIN for each product, checks prior use, and gives the company dashboard product, time, and location context for authentication activity. This creates a brand-controlled link between a physical pack and an authentication record.
xBarkod does not replace production-order, quality, inventory, or dispatch systems. Its value grows when the authentication identity maps to the records described in the contract manufacturing traceability guide. Evaluate the approach with one product family and test allocation, application, waste, returns, and field authentication together.
Which acceptance tests should the pilot pass?
A useful pilot must prove more than successful scanning. It should exercise normal and exception paths in a real production order. Pair the digital checks with the physical controls in the security-label application guide.
- The correct identity appears on the approved product and packaging version.
- A previously allocated identity cannot be assigned again.
- A printing error is blocked and its disposition recorded.
- An unused label follows a visible return or destruction process.
- First-use and repeat-use results are understandable.
- An unexpected event can be traced to production and dispatch evidence.
- An unauthorised user cannot change identity status.
Brand, factory, quality, and operations teams should approve the acceptance criteria together. A failure may require a change to the receiving desk, work instruction, or role permissions rather than a software setting. The purpose of the pilot is to expose the weakest handoff at limited scope before extending the system.
Frequently Asked Questions about brand protection in contract manufacturing
What does brand protection in contract manufacturing mean?
It is the discipline of governing brand-owned product definitions, packaging, codes, security labels, and dispatch evidence through explicit permissions and records. It aims to prevent uncontrolled use of legitimate identities and to make field incidents reviewable, not merely to search for fake goods.
Is every production overrun a trademark infringement?
No. A conclusion depends on the contract, approved tolerances, release authority, sales rights, and applicable law. Operationally, define the tolerance in advance, segregate unapproved output, and allocate brand identities only to goods that the brand has accepted for the authorised route.
Can the contract manufacturer store security labels?
Yes, physical custody may remain at the factory, but receipt, access, use, waste, remaining stock, and return permissions should be documented. The brand needs visibility into which range belongs to each order and how unused identities are closed.
Is a standard product barcode enough for authentication?
No. A standard product barcode can repeat across many units of the same trade item. Item-level authentication needs an identity tied to a particular pack or product. A concealed PIN and prior-use check add context when a visible QR graphic may be copied.
Does a repeated code prove factory overproduction?
No. A customer may rescan, a support agent may test, or the visible code may have been copied. Review the order, allocation, product image, time, location, dispatch, and support context before drawing a conclusion about the source.
Does xBarkod audit the contract manufacturer?
No. xBarkod provides brand-controlled product authentication and visibility into authentication activity. It does not replace supplier audits, quality release, or contract management. Its records support investigation when connected to the brand's production and shipment evidence.
Conclusion: close the order together with its identities
The strongest control is the ability to show which approved product, packaging version, order, and shipment stands behind every identity. When label allocation, waste, unused stock, and accepted goods share one close process, field signals can be reviewed faster and with fewer assumptions.
Start with one product family and place the existing manufacturer and brand-owner responsibilities beside the identity lifecycle. If the business cannot show who allocates, applies, blocks, releases, and investigates each identity, close that governance gap before scaling.
More Articles
Product Authentication Code Mapping: A Daily Workflow for Private Label Brands
Learn how private label brands map authentication codes to products, manage QR and hidden PIN checks, review dashboard activity, and investigate suspicious use.
Product Authentication System Setup: A Daily Workflow for E-Commerce Brands
Set up product authentication with clear records, unique codes, QR and hidden PIN checks, dashboard review, and suspicious-use handling for e-commerce brands.
Product Authentication Location Tracking: From Setup to Daily Review
Build product authentication location tracking with clear permissions, data quality, daily review, privacy controls, and practical pilot criteria.